Disaster Recovery Posture Management

Find what breaks your recovery before an attacker does.

Recuperer plugs into the tools you already run, like AWS Backup, GuardDuty, Elastio and Vanta, and connects what each one knows into a picture of what every service needs to come back. Then it scores the risk and fixes the gaps. Discovery is read-only; changes run only where you allow them.

A GuardDuty alert or a failed backup job means more when you know which service it puts at risk.

PLATFORMS: AWS FORENSICS: Elastio, GuardDuty EVIDENCE: Vanta, Security Hub
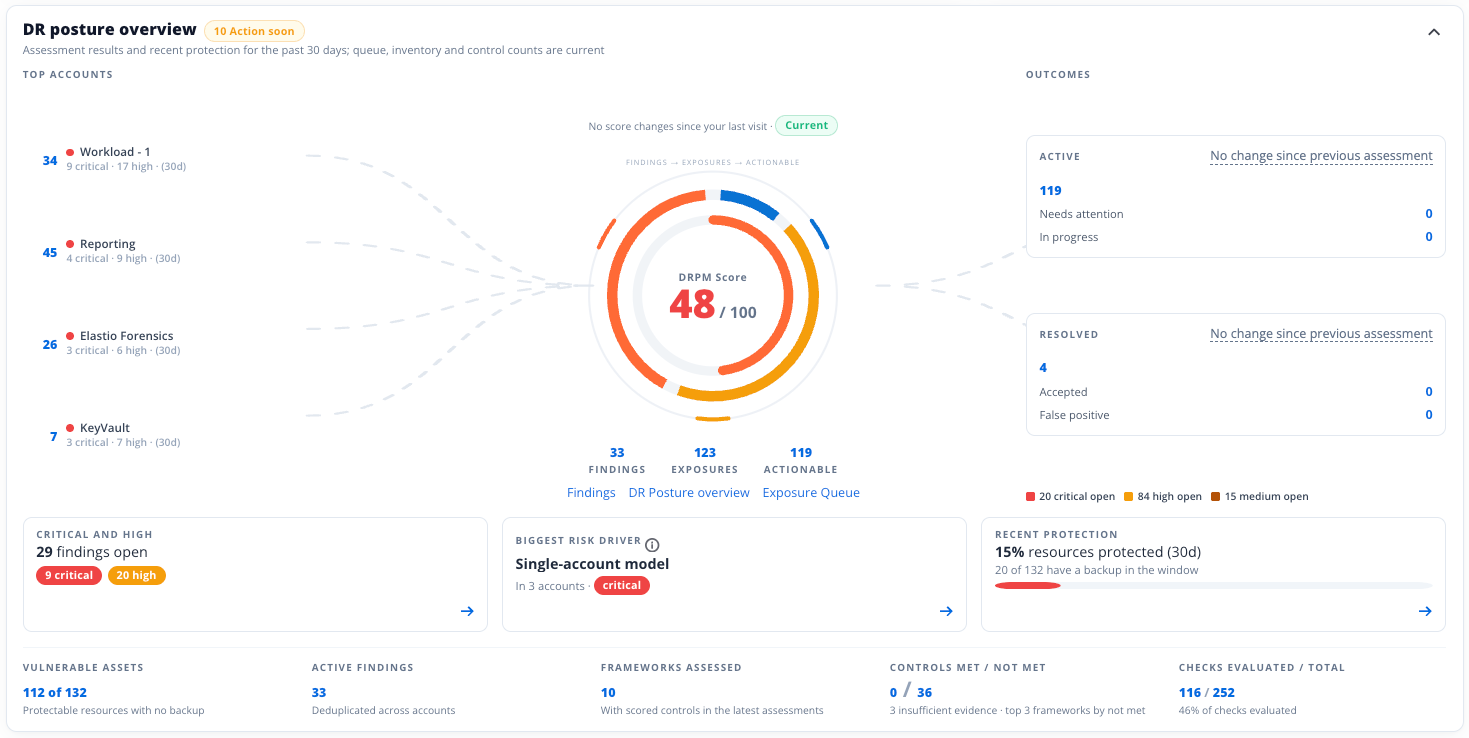
LIVE DR POSTURE SCORE: 48 / 100
Layer 01 · Map Read-only

Digital Twin

Data, keys, roles, network and vaults, per service.

1,284 Resources 36 Affinity Groups
Layer 02 · Score Risk

DR Posture Score

Ransomware loss paths, mapped to 14 frameworks.

20 Critical Open 84 High Open Vanta: Synced
Layer 03 · Fix Logged

ResOps

Low-risk fixes run on their own. The rest wait for approval.

Auto-fixed: Backup tags Needs approval: Vault Lock
Digital TwinYour existing data, connected per service
DR Posture ScoreOne number per service
ResOpsAutonomous fixes, with proof
ChronoAsk questions, get sourced answers
How it starts

From a read-only role to your first fix.

Nothing in your account changes until you approve it.

01 · Connect

Add a read-only role

For one AWS account or a whole Organization.

02 · Map

Build the Digital Twin

Grouped by what recovers together.

03 · Score

See your DR Posture Score

See which gaps put recovery most at risk.

04 · Fix

Close the gaps

Approve the changes you want. Low-risk ones can run on their own.

Why now

A finished backup isn’t a recovery.

A backup tool can tell you a snapshot finished. It can’t tell you the service will come back.

Minutes

Attackers go for the backups

Ransomware crews delete recovery points and disable keys before they encrypt.

A yearly review won’t catch it
Drift

Your cloud changes every day

A good backup won’t help if a secret, route or IAM role it needs has changed.

The map updates as you deploy
What’s different

Each tool sees part of the picture. Recuperer connects the dots.

Tool
What it tells you
What Recuperer adds
Backup tools
The backup job completed.
Whether the service comes back, and in what order.
Config scanners
One resource at a time.
How weak links chain across resources and accounts.
Runbooks & tabletops
A point-in-time review.
A map and score that stay current.
Alerts & tickets
A list of problems.
A fix you can preview, approve and audit.
How it works

Map, score, fix. Then again.

The loop

1. Map → 2. Score → 3. Fix

It reruns after every change.

Three-layer repeating DR posture management loop diagram ↻ RE-CHECKED AFTER EVERY CHANGE LAYER 01 · MAP Digital Twin What each service depends on. LAYER 02 · SCORE DR Posture Score Loss paths and 14 frameworks. LAYER 03 · FIX & PROVE ResOps Workflows Previewed, approved, logged.
Layer 01 · The Digital Twin

See what each service needs to come back.

A service is only back when everything it depends on is back. The Digital Twin joins your cloud inventory, backup jobs, security findings and scan results into one map of compute, databases, keys, roles and backup copies, and the order they recover in.

  • Current: Updates across accounts and Regions as you deploy.
  • Bottlenecks: The one key, secret or DNS zone that many services share.
  • RTO and RPO: Restore times estimated from data size and copy lag.
Digital Twin dependency graph showing live service relationships DIGITAL TWIN · CRITICAL PAYMENT SERVICE TOPOLOGY LIVE SYNC · 12s Core Payment API (Tier-0) EKS Cluster MULTI-AZ · READY Aurora Global DB RPO: 45s · LOCKED Terraform / KMS SINGLE-REGION KEY Air-Gapped Vault (eu-west-2) VERIFIED RECOVERY PATH Cross-Account Decrypt Role HIDDEN RECOVERY BLOCKER
Recoverable path Bottleneck
Layer 02 · The DR Posture Score

Score the risk to recovery, not to single resources.

Checks chain into loss paths, like “an outside role can delete backups in an unlocked vault”. Each maps to industry, regional and national frameworks, from SOC 2 and PCI DSS to DORA, NYDFS and APRA CPS 234, so you align to a new regulation faster.
  • Shared risk: A weak role or key counts against every service that uses it.
  • One score: RPO and RTO, immutability, isolation and restore testing.
  • Compliance: Control status can sync to Vanta.
Recuperer DR posture dashboard showing score overview, workloads, findings, and active threat exposures
LIVE CONSOLE PREVIEW DRPM Score: 48/100 · 20 Critical Open
Layer 03 · ResOps

Autonomy you can prove.

AI agents and automation are only useful if they can’t go rogue. ResOps acts only inside the limits you set for each account. Anything that touches a security boundary waits for a person, and every action is previewed and signed, so you can show what ran and why.

  • Automatic: Reversible fixes like backup tags or PITR, where you’ve opted in.
  • Approved: Vault Lock and key policies, optionally as Terraform.
  • Evidence: The finding, decision, run and new score are signed.
RESOPS · TWO PATHS GUARDRAILS · SIGNED LOG
● Automatic Low-risk, reversible

Backup tags, PITR, key rotation, adding to a backup plan.

◆ Approval Security boundaries

Vault Lock, key policies, cross-account copies.

01
Find the gap Costs 9 points of DR Posture Score
Detect
02
Pick the path Automatic or approval, by policy
Route
03
Apply and verify Scoped to your account; checked after
Execute
04
Prove it Signed evidence; the map and score update
Prove ↻
Tamper-evident Then the loop runs again
One finding, end to end

A vault without Vault Lock.

How one finding moves from detection to a signed record.

01 · Finding The gap Recovery points can be deleted before their retention ends.
02 · Evidence The check and the data The check, its data, and the affected services.
03 · Simulate Read-only preview The proposed change, as a diff, before anything runs.
04 · Approve Your decision Vault Lock always needs a person to approve it.
05 · Prove Signed record The decision, the run and the new score are recorded.

Illustrative example. Details vary by account and finding.

In the console

Day-to-day tools

Chrono AI assistant

Ask about your posture.

Answers from your data, with sources.

Exposure queue

Work through findings.

Each with a fix, a preview and the approvals it needs.

Restore tests & clean copies

Test restores.

Run restore tests and drills, and find the newest clean recovery point.

Backup FinOps

Cut backup spend.

Spend by service and account, and savings that won’t lower your score.

Integrations

Works with the data you already have.

Cloud

Your estate

Read-only discovery across accounts, Organizations and Regions.

AWS AWS Backup Coming soon Microsoft Azure Google Cloud Kubernetes
Forensics & context

Is the backup clean?

Malware and ransomware verdicts on your backups, tied to the services that rely on them.

Elastio Amazon GuardDuty Amazon Inspector Coming soon ServiceNow CMDB Veeam
Evidence & alerts

Where the proof goes

Reports, control status, findings and run events.

Vanta AWS Security Hub Webhooks Coming soon Datadog
For your teams

Who uses it

CISO and resilience leads

A score for each critical service.

Against ransomware and the regulations in each region you operate in.

Platform teams

You set what runs on its own.

Per account. Security changes always need approval.

GRC and audit

Evidence mapped to your frameworks.

Exported to Vanta or Security Hub.

SRE and BCDR

Know the recovery order in advance.

Find circular dependencies and single-Region keys before an outage does.

Get started

Start with an assessment.

We connect read-only, map your services and walk you through the results.

Nothing in your account changes.

Dependency map For one critical service, with its bottlenecks.
Score and findings Mapped to the industry and regional frameworks you report on.
Fix plan What can run automatically, and what needs approval.

Request an assessment

We’ll reply to set up a time.

Read-only IAM role · No changes to your accounts